

Writing a cargo security policy that satisfies CTPAT, ISO, and internal audit expectations requires more than naming a standard. The policy must tell people exactly how cargo is protected, who owns each control, what evidence is retained, and what happens when a seal, shipment, or partner fails a check. For a practical starting point, review STiER's supply chain compliance and security guide, then use the framework below to turn security expectations into an operating document.
Request a quote for high-security seals and compliance documentation support.
Why does CTPAT require a written cargo security policy?
CTPAT is a voluntary U.S. Customs and Border Protection program, but participation carries an expectation that security practices are documented, implemented, reviewed, and improved. CBP's CTPAT minimum security criteria are tailored to an organization's role in the supply chain. A policy gives the company a controlled way to show how those criteria operate in its own facilities, lanes, and partner network.
A strong policy does not claim that CTPAT approval is automatic or that one seal makes a shipment compliant. Instead, it connects physical security to management responsibility and documented verification. It should explain how the organization:
- Assesses cargo, facility, route, partner, and personnel risks.
- Controls seal purchasing, storage, assignment, application, inspection, removal, and disposal.
- Records seal numbers and exceptions so a shipment can be traced from loading through receipt.
- Verifies business partners and addresses subcontracted cargo-handling activities.
- Reviews incidents, corrective actions, and policy performance when risks or operations change.
CBP's recommended seal procedures also distinguish between minimum criteria and additional best practices. Your policy should make that distinction visible. Mark mandatory controls as requirements, identify risk-based enhancements separately, and assign an owner for every recurring activity.
What sections should your cargo security policy include?
Write the policy so an employee, auditor, or manager can find the answer to five questions: what is protected, who is responsible, how is the control performed, what record proves it happened, and what is the response to an exception?
1. Scope and security objectives
Define the cargo, facilities, modes, trade lanes, distribution centers, and third parties covered by the policy. State the objectives in operational language, such as preventing unauthorized access, detecting tampering, preserving chain of custody, and supporting timely investigation. Include related functions such as procurement, receiving, transportation, security, quality, and information technology where they affect cargo integrity.
2. Roles, authority, and escalation
Name the executive sponsor and the person responsible for maintaining the policy. Clarify who may order, issue, apply, inspect, or destroy a seal. Establish an escalation path for a broken seal, an unexplained number mismatch, missing inventory, an unapproved carrier, or a suspected security event. Make it clear that employees may stop or hold a shipment when a defined control fails.
3. Risk assessment and control selection
Describe how the organization identifies threats and prioritizes controls. Consider origin, route, cargo value, facility access, dwell time, seasonal volume, geopolitical exposure, and the security maturity of each partner. The output should drive choices such as high-security bolt seals for container doors, cable seals for suitable access points, or indicative seals for lower-risk applications. Do not describe every seal as interchangeable.
4. Seal control and chain of custody
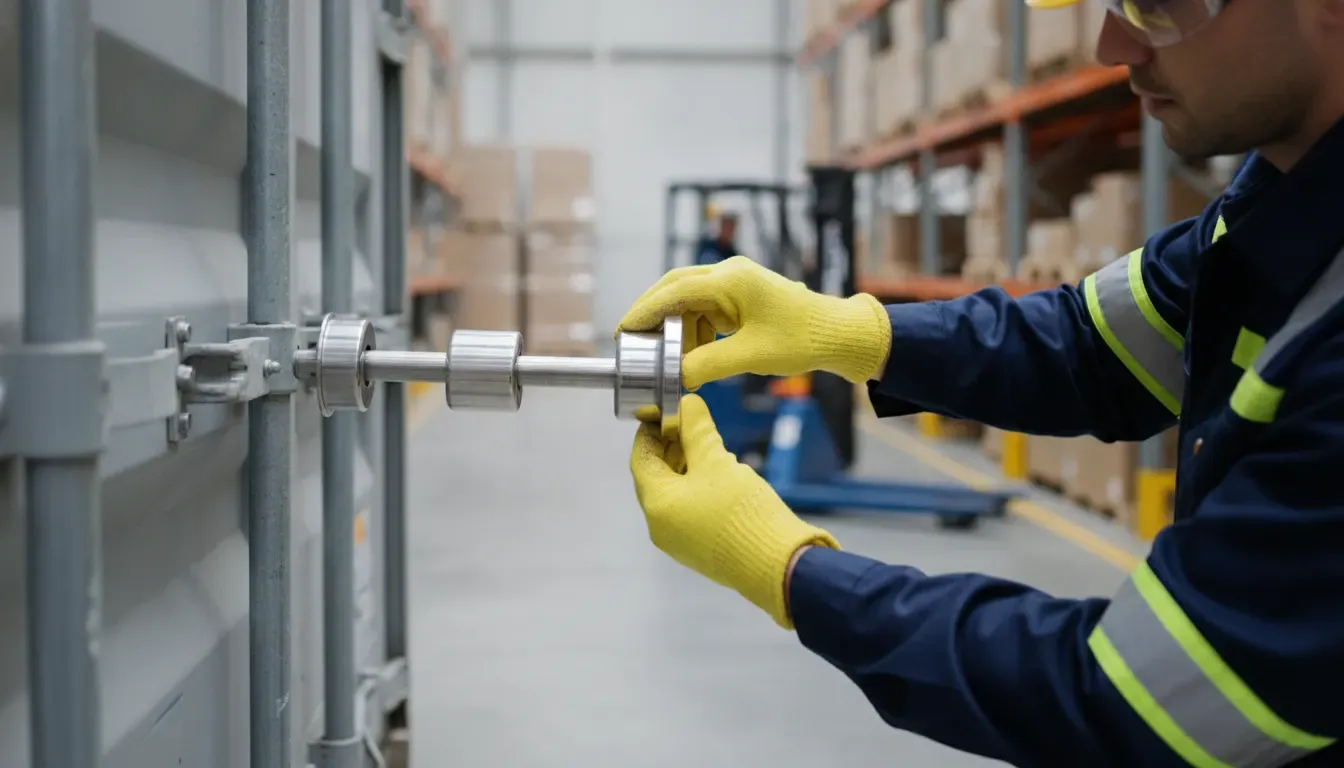
Document how serialized seals are received, counted, stored, issued, applied, inspected, and reconciled. Define the required fields for a seal log, including serial number, shipment or container reference, person applying the seal, date and time, location, carrier, destination, inspection result, and exception notes. State how unused, damaged, removed, or voided seals are controlled.
For high-security container seals, specify the required standard and the evidence procurement must retain. ISO 17712:2013 establishes uniform procedures for classifying, accepting, and withdrawing mechanical seals used on freight containers. A policy should therefore require current supplier documentation and a check that the selected product matches the shipment and risk profile. STiER's security seal record-keeping guide provides a related framework for retention and audit readiness.
5. Partner, facility, and incident controls
Explain how carriers, brokers, manufacturers, warehouses, and other partners are approved and monitored. Include minimum contract language, security questions, evidence requests, and review frequency. Add facility controls for visitor access, loading areas, trailer parking, key or lock management, and shipment staging. Finally, define incident reporting, evidence preservation, investigation, customer notification, and corrective action.
How should ISO 17712 and ISO 9001 shape policy language?
CTPAT, ISO 17712, and ISO 9001 address related but different parts of a security program. Treating them as synonyms creates vague requirements and weak audit evidence.
| Reference | What it addresses | How to reflect it in the policy |
|---|---|---|
| CTPAT | Supply chain security practices and risk-based controls | Define responsibilities, partner controls, security procedures, reviews, and evidence. |
| ISO 17712 | Classification and acceptance of mechanical freight-container seals | Specify seal selection, supplier evidence, application, inspection, and records. |
| ISO 9001 | Quality management and controlled documented information | Control approvals, revisions, training, corrective action, and performance review. |
Use precise verbs. Say who shall perform a control, when it occurs, what input is required, what record is created, and who reviews exceptions. Avoid statements such as "secure all cargo appropriately" unless a procedure or work instruction defines what "appropriately" means.
ISO's guidance on documented information emphasizes that documentation should support the organization's processes and provide evidence that they operate as intended. The policy is the governing document. Detailed seal-application steps, receiving checklists, and incident forms can sit beneath it as controlled procedures and records.
For product selection, link the policy to approved specifications rather than copying unsupported performance claims into the document. A procurement appendix can identify the required ISO 17712 classification, serialization format, marking requirements, approved suppliers, and certificate records. STiER's seal certification comparison can help teams separate the purpose of each certification when reviewing suppliers.
How can internal audits test whether the policy works?
An internal audit should test implementation, not just whether the policy file exists. Build an audit trail from the written requirement to a sample of real shipments, records, interviews, and corrective actions. The auditor should be able to select a container or shipment and follow the evidence in both directions: from the seal record back to issuance, and from the shipment record forward to receipt and inspection.
Use a control-to-evidence matrix
For each policy control, record the requirement, responsible owner, evidence source, sample method, result, and corrective action. Examples include:
- Seal inventory: compare physical stock to the controlled issue and disposal log.
- Application: match a sample of seal numbers to shipment records, photos, loading records, or inspection entries.
- Receiving: check that personnel record the seal condition and number before opening cargo.
- Partner oversight: confirm that high-risk carriers or facilities were reviewed at the required interval.
- Training: verify current training completion and observe whether employees follow the procedure.
- Exceptions: trace a broken or mismatched seal from notification through disposition and corrective action.
Use the audit findings to improve the policy. If employees follow a different process because the document is impractical, revise the controlled procedure and retrain them. If a control is repeatedly missed, investigate whether the owner, system, workload, or risk assumption is wrong. ISO's internal audit guidance is useful for keeping the audit focused on process effectiveness and evidence rather than paperwork alone.
How should you distribute and train staff on the policy?
Approval is not implementation. Publish the current policy in a controlled location, identify the revision and effective date, and remove obsolete copies from work areas. Translate or adapt supporting work instructions when employees operate in different languages or facilities, while preserving one controlled requirement set.
Training should be role-specific. A loader needs to know how to inspect the door, apply the correct seal, and record the number. A receiver needs to know how to compare the seal to the record and escalate a discrepancy. A buyer needs to know how to confirm classification, serialization, supplier documentation, and change notifications. A manager needs to know how to review trends and authorize corrective action.
Use short demonstrations, scenario practice, and observed competency checks for high-risk steps. Retain the training record, trainer, date, version of the procedure, attendees, and any remediation. Retrain when the policy changes, a new seal or system is introduced, an incident occurs, or an audit identifies a recurring gap.
For approved high-security bolt seals and related products, STiER's bolt seal collection is a useful starting point for matching the physical control to the cargo application. The policy should still require the responsible team to confirm the product specification and current supplier documentation before use.
What should you review before approving the policy?
Before approval, run a practical readiness review with security, logistics, quality, procurement, and operations. Confirm that the policy:
- Names the covered cargo, sites, lanes, partners, and accountable owners.
- Defines seal selection, serialization, storage, application, inspection, reconciliation, and disposal.
- Separates CTPAT security controls from ISO 17712 product requirements and ISO 9001 document controls.
- Specifies the records that prove each control occurred and the retention owner.
- Explains how exceptions, incidents, partner failures, and corrective actions are handled.
- Maps each control to an internal audit test and a measurable review point.
- Includes current training, revision control, approval, and distribution requirements.
A cargo security policy becomes audit-ready when employees can use it during a real shipment, managers can verify it with records, and auditors can test it without relying on informal explanations. Keep the policy direct, connect each requirement to an owner and evidence source, and update it when the cargo network or risk profile changes.
Contact STiER to build a documented, CTPAT-focused seal program for your supply chain.